Last updated: 2026-11-06
nis2-readiness.de is run by Blackfort Technology UG (haftungsbeschränkt), Ernst-Robert-Curtius-Straße 8A, 53117 Bonn, Germany. The company has been registered in the commercial register of the Bonn local court since 2017 (HRB 23120) and is owner-managed. We work in information security, compliance and technical implementation: regulatory classification and implementation in the systems come from the same project. Founder and Managing Director is Christian Gebhardt.
What NIS2-Readiness is
NIS2-Readiness brings together our services for implementing NIS2. It is aimed at mid-sized companies with small IT teams that fall under NIS2, and at their suppliers. We care about concrete results: technical measures, working processes and evidence that stands up to management and to an audit.
The service behind it is consulting on NIS2 implementation, with the NIS2 gap analysis as the entry point.
Founder and Managing Director: Christian Gebhardt
Christian Gebhardt, Managing Director since 2017
| Period | Role | Company |
|---|---|---|
| 2021-2024 | Deputy CISO | Gothaer Solutions GmbH |
| 2020-2021 | Information Security Officer | Gothaer Solutions GmbH |
| 2021-2023 | Managing Director | ArcSin GmbH |
| 2017-2019 | Audit Specialist | Deutsche Bank Group |
| 2015-2016 | Security Consultant | TÜV Trust IT |
| 2014-2015 | IT Security Consultant | exceet Secure Solutions |
| 2007-2014 | Working student, IT Solution Architect, Junior Systems Engineer | BWI Informationstechnik |
- Permanent member of the AI Expert Working Group
Alliance for Cyber Security / BSI - Co-author: “Guidelines for Penetration Testing of Large Language Models” (ACS/BSI)
Christian Gebhardt founded Blackfort Technology in 2017, alongside his role as an audit specialist at Deutsche Bank.
The professional background he brought with him continues to shape how Blackfort works today. He started as a working student at BWI Informationstechnik, the IT service provider of the German Federal Armed Forces, and stayed for seven years. From 2011 he worked there as an IT Solution Architect and systems engineer, responsible for directory services, identity and access management and the BWI PKI based on the PKI of the German Armed Forces. This was followed by roles at exceet Secure Solutions in the Gematik telehealth infrastructure with a focus on PKI and Hardware Security Modules, and at TÜV Trust IT, where he led ISO 27001 ISMS build-out projects at municipal critical infrastructure organisations.
Deutsche Bank opened the perspective of independent review: audit leadership in highly regulated domains - BAIT, MaRisk, ZAG, KRITIS - covering topics such as information security management, payment processing, PKI and data centre security. This experience at times revealed just how far apart documented requirements and lived practice can be.
After his role as Information Security Officer at Gothaer Solutions GmbH, he became Deputy CISO in 2021, leading the information security team with a direct reporting line to the IT board member.
In parallel, from 2021 to 2023 he served as Managing Director of ArcSin GmbH, a company specialising in artificial intelligence and cryptography with a focus on massively parallel processing in distributed systems - an early engagement with AI architecture well before the topic became mainstream for security organisations.
In the field of AI security, he is a permanent member of the AI Expert Working Group of the Alliance for Cyber Security (ACS/BSI). He co-authored the ACS “Guidelines for Penetration Testing of Large Language Models” (2025) and wrote its first draft.
How we work
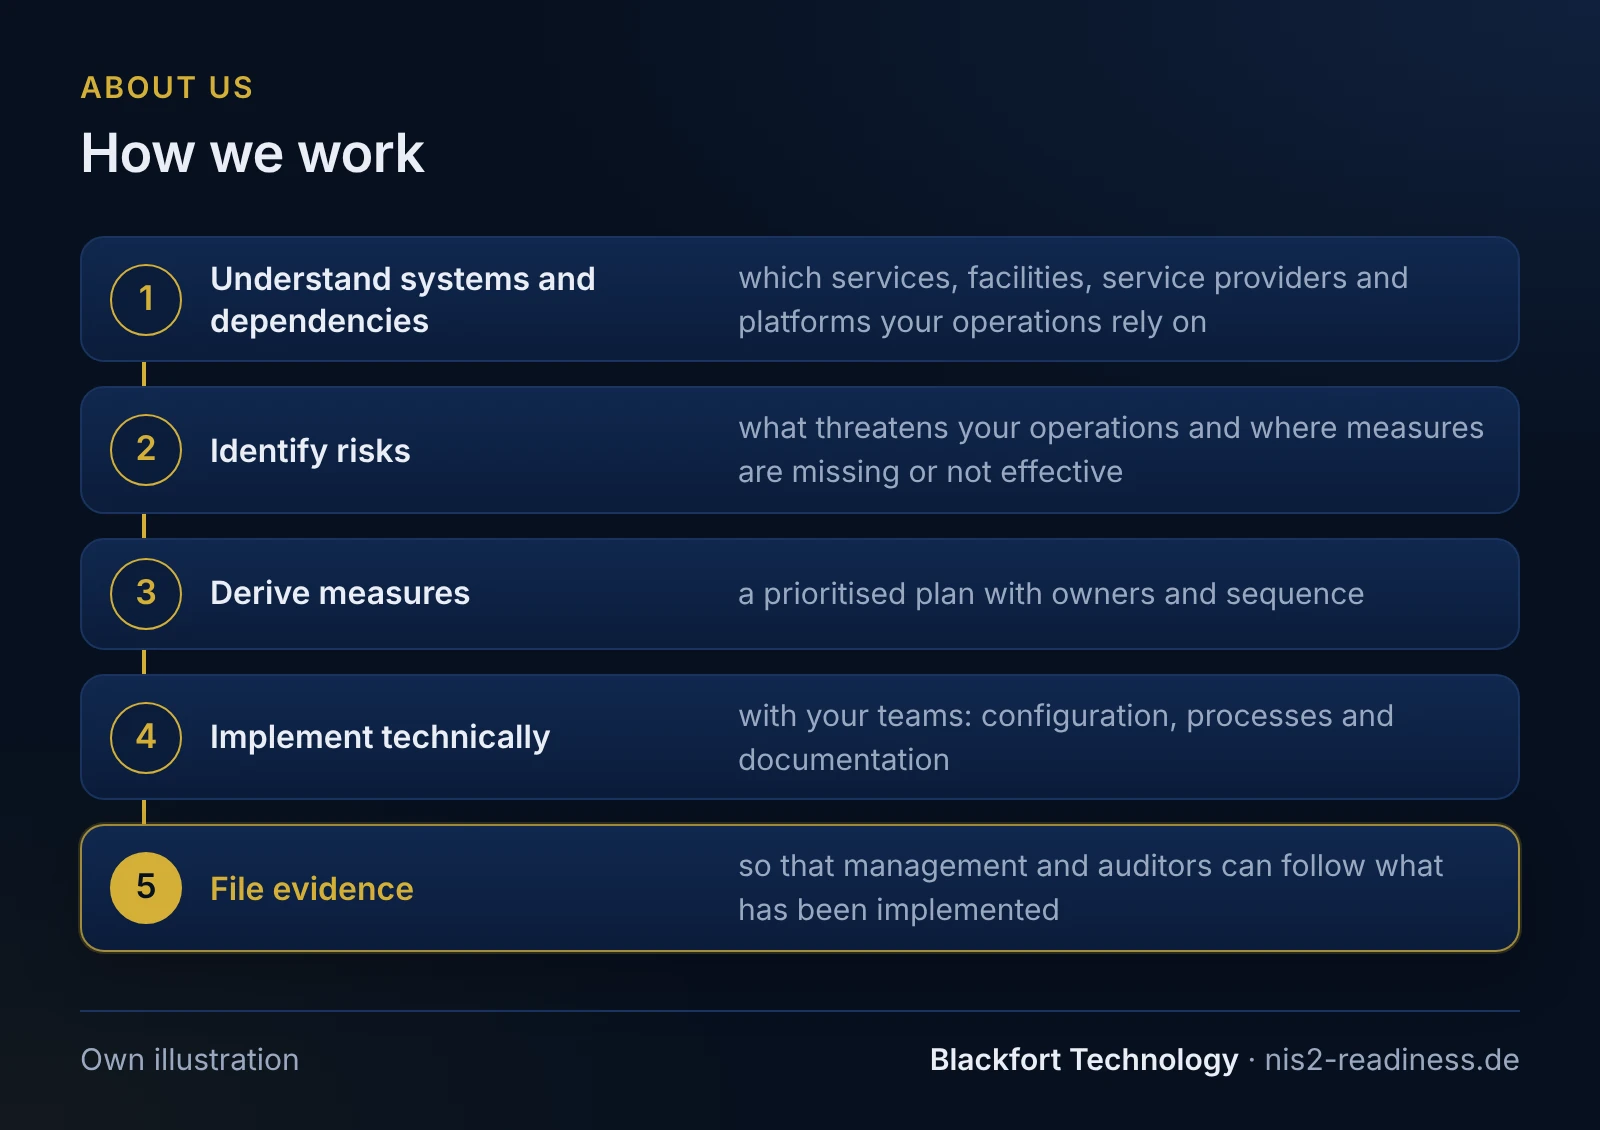
Our approach has five steps:
- Understand systems and dependencies: which services, facilities, service providers and platforms your operations rely on.
- Identify risks: where measures are missing or not effective.
- Derive measures: a prioritised plan with owners and sequence.
- Implement technically: together with your teams we implement configuration, processes and documentation.
- File evidence: so that management and auditors can follow what has been implemented.
Your enquiry is received by Christian Gebhardt as founder and Managing Director; who works on the project is set out in the proposal. We work in German or English, by video conference and on site where the project requires it.
Why we do not name clients
We do not name clients on this website because confidentiality is part of consulting. Instead of references, we show our method and sample results.
Blackfort Technology is a partner of Tenable, Rapid7 and DigiCert. These partnerships concern security tools and certificate services.
What you can expect from us
- We back statements on laws and regulations with the provision and the date of the version we checked.
- We say what the law requires, what we recommend and what is an example, and keep these visibly apart.
- On NIS2 and other legislation we provide general information. The legal assessment of your case belongs with a lawyer.
Frequently asked questions
Does Blackfort Technology work on behalf of the BSI?+
Where is Blackfort Technology based?+
Read more
Sources
- Blackfort Technology: company website (retrieved 2026-11-06)
- Blackfort Technology: About us (German version) (retrieved 2026-11-06)
- Blackfort Technology: About Us (Christian Gebhardt’s background) (retrieved 2026-11-06)
This content provides general technical and organisational information and does not constitute legal advice (no legal services within the meaning of the German RDG).